Keeping Credentials Secure While Giving AI Agents More Autonomy

AI agents become more useful when they can authenticate to the services involved in their work. A development agent might need access to a Git host, a deployment platform, or a database. Those credentials also give mistakes consequences: a token printed in terminal output can enter the agent’s conversation, and a misplaced file can end up in a commit.
The aim is to let tools authenticate while keeping secret values out of model-visible inputs and outputs.
Start with restricted files
On Linux and macOS, restrict access to each credential file:
chmod 600 path/to/credentialsThe three digits describe permissions for the owner, group, and everyone else. The 6 combines read permission (4) and write permission (2). Both zeros deny access to the group and other users through these permission bits; existing ACL grants can allow additional access. The process using the credential must run under the appropriate account.
On Windows (NTFS), use icacls in Command Prompt:
icacls "path\to\credentials" /inheritancelevel:r /grant:r "%USERDOMAIN%\%USERNAME%:RW"This removes inherited access and grants your account read/write. Remove other explicit grants if present.
It helps protect a file from other ordinary users on the machine. It does not prevent an agent running as the owner from reading and printing its contents, or stop sufficiently privileged processes from accessing it. Create new credential files with restrictive permissions from the outset; changing permissions afterward cannot undo earlier exposure.
Encryption adds another responsibility
You can encrypt the strings inside credential files and build a helper that decrypts them when needed. That improves protection of the stored values, but introduces another secret: the decryption key. This is helpful for files that contain environment variables so one file can contain multiple credentials but if the key sits beside the encrypted file and the same process can read both, the protection is limited. Decrypted values can still escape through logs or tool output. You now also need to manage encryption, key storage, and credential updates.
OpenBao changes the credential workflow
OpenBao is an open-source secrets manager forked from HashiCorp Vault. The project sits under the Linux Foundation’s Open Source Security Foundation, or OpenSSF. That provides open governance; secure deployment and operation remain the operator’s responsibility. OpenSSF’s introduction describes the project and its foundation involvement.
Instead of scattering credentials across development machines, you can host an OpenBao instance that encrypts stored secret values and controls access through authentication and policies.
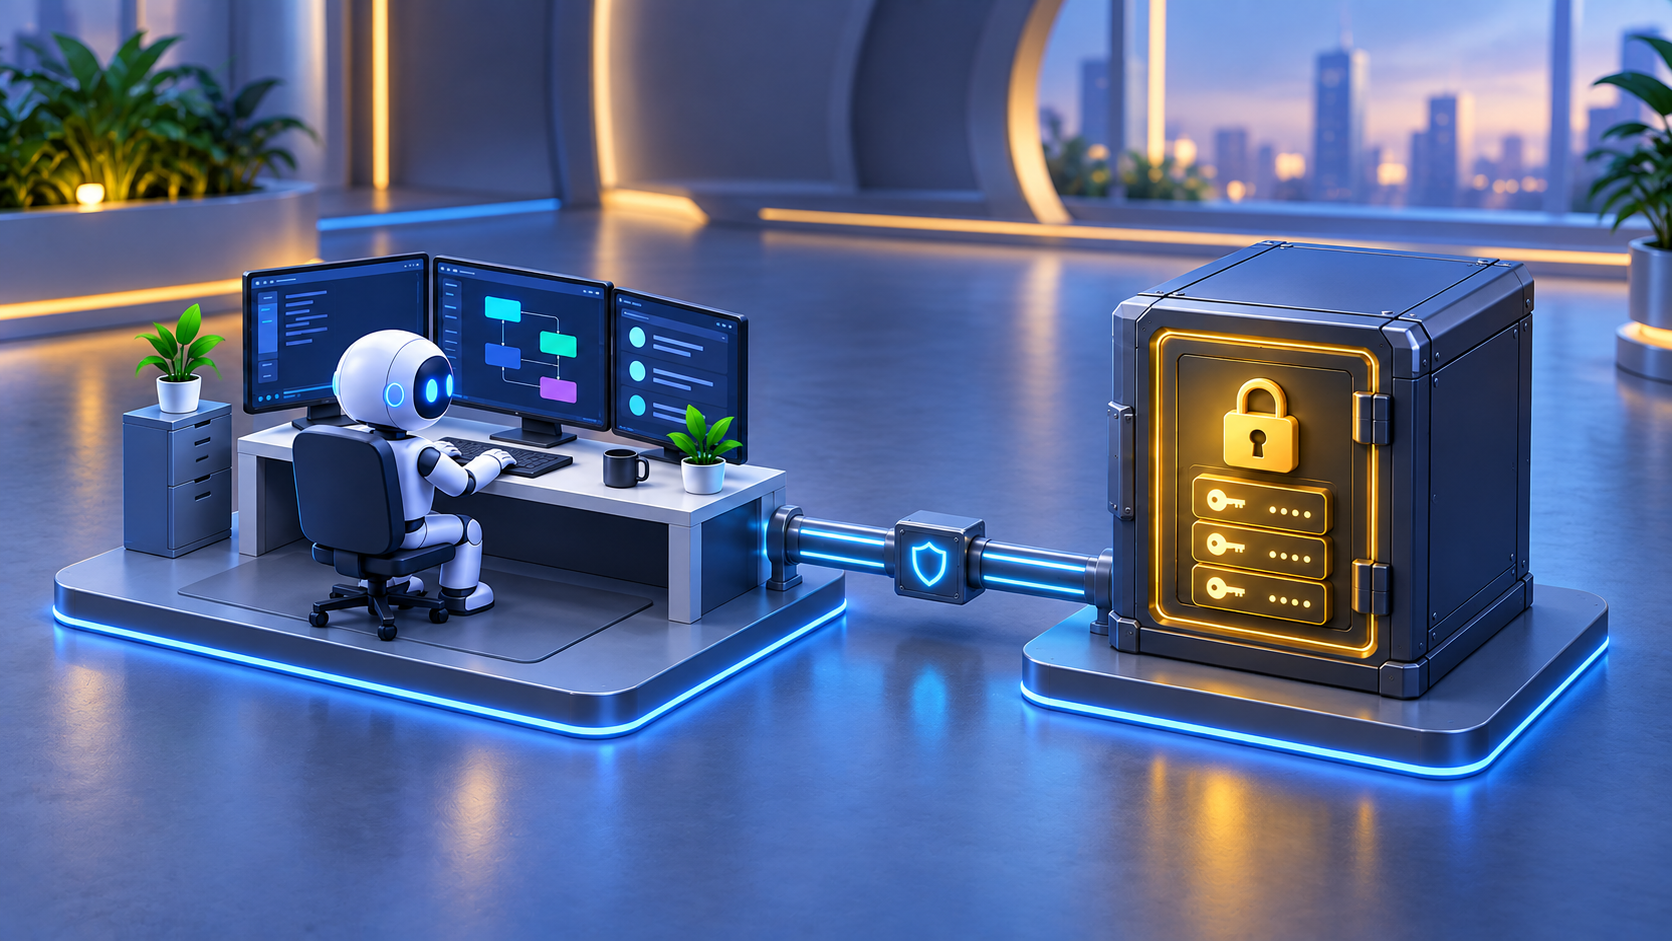
Consider an agent checking a deployment. It calls a helper that authenticates to OpenBao with narrowly scoped access, retrieves the required credential, queries the deployment service, and returns selected status fields. The token stays out of the conversation, including error output.
An agent skill can make this a repeatable workflow. The openbao-ops skill pairs an agent with a configured credential helper for checking metadata, importing or updating credentials from protected files, and adjusting scoped access policies. The helper handles authentication internally and returns useful results without putting secret values in the conversation.
For extra isolation, run the credential broker in a Docker container under a dedicated service account, with a read-only filesystem and only the credential files and local socket it needs. Keep Docker administration outside the agent’s control: access to the Docker daemon or privileged host access can defeat that separation. Docker complements the dedicated VM described below. Docker’s security guidance explains these boundaries.
Agents can help with credential and identity management too. With the appropriate authorization and integration, they can provision task-specific roles, grant the access a workload needs, and retire access when a task or machine is no longer needed. OpenBao’s policies give each identity a defined set of permissions.
OpenBao also provides audit logs and temporary credentials for supported services, making access easier to track and retire. Static API tokens can be managed centrally, with rotation coordinated through their issuing services. This lets you delegate routine credential work through established tools rather than handling every token yourself.
Give autonomy an isolated workspace
Disabling an agent’s approval prompts lets it work with fewer interruptions and increases what it can do without supervision. A carefully isolated VM reduces exposure of personal documents, browser sessions, and unrelated projects compared with running that workflow directly on your personal machine.
Secure credential storage works well alongside a dedicated virtual machine. The VM provides a separate operating system and workspace where an agent can install dependencies, change files, and run development tools.
Keep OpenBao outside the agent-controlled VM. Give the VM access only to the secrets and services needed for its task. Avoid mounting your entire home directory, forwarding broad credentials, or granting unrestricted access to your private network. Otherwise, those connections can undermine the separation you intended.
For development work that needs high autonomy, combine an isolated workspace with narrowly scoped credential access and tools that keep secrets out of their responses. That gives the agent room to work while limiting what an error can expose or affect.